JustWhat Security Audit · by Vinny
Find what attackers look for first, right inside WordPress.
Out-of-date WordPress, plugins and themes, risky settings, missing security headers, exposed files and known vulnerabilities, each with why it matters and how to fix it. It only reports: it changes nothing on your site.
WordPress 6.4+ and PHP 8.1+. Use it alongside your security plugin and backups; it isn't a firewall or malware scanner.
Screenshots
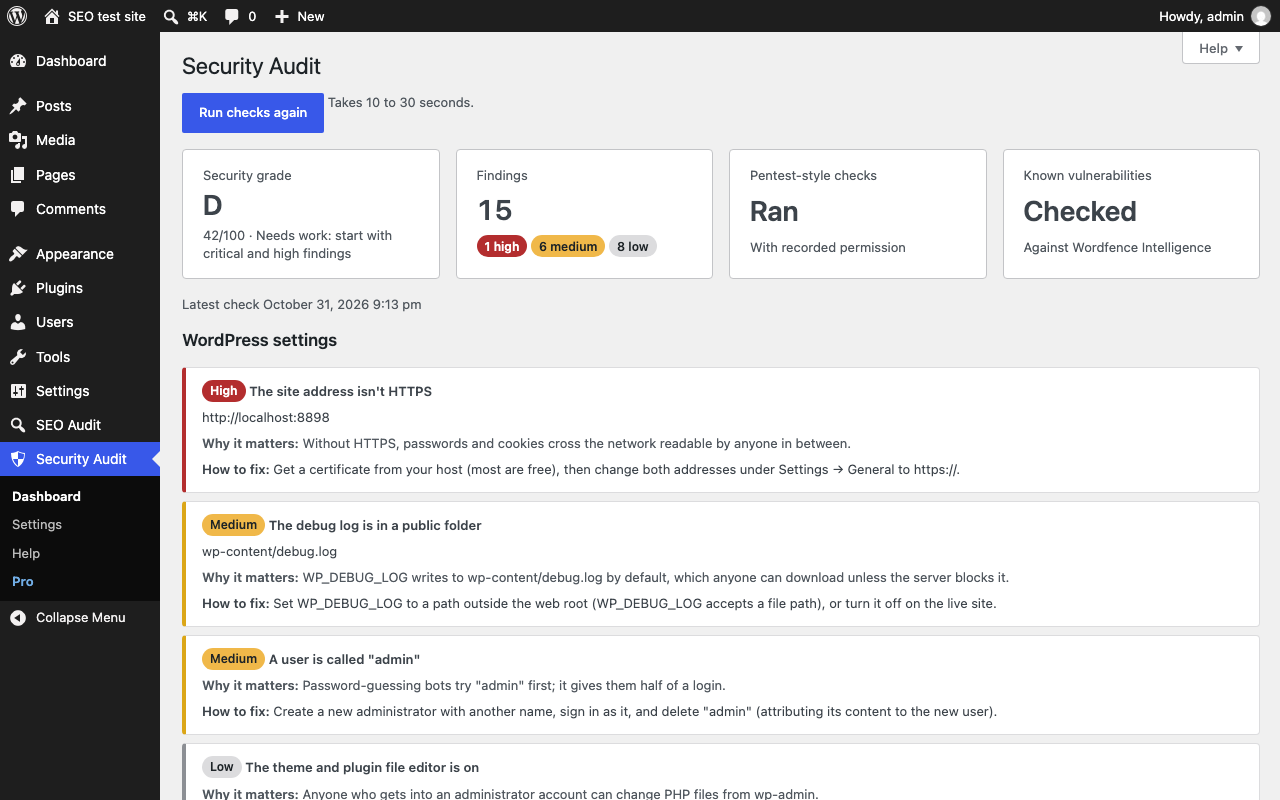
Dashboard: the grade, findings by severity and which kinds of checks ran. 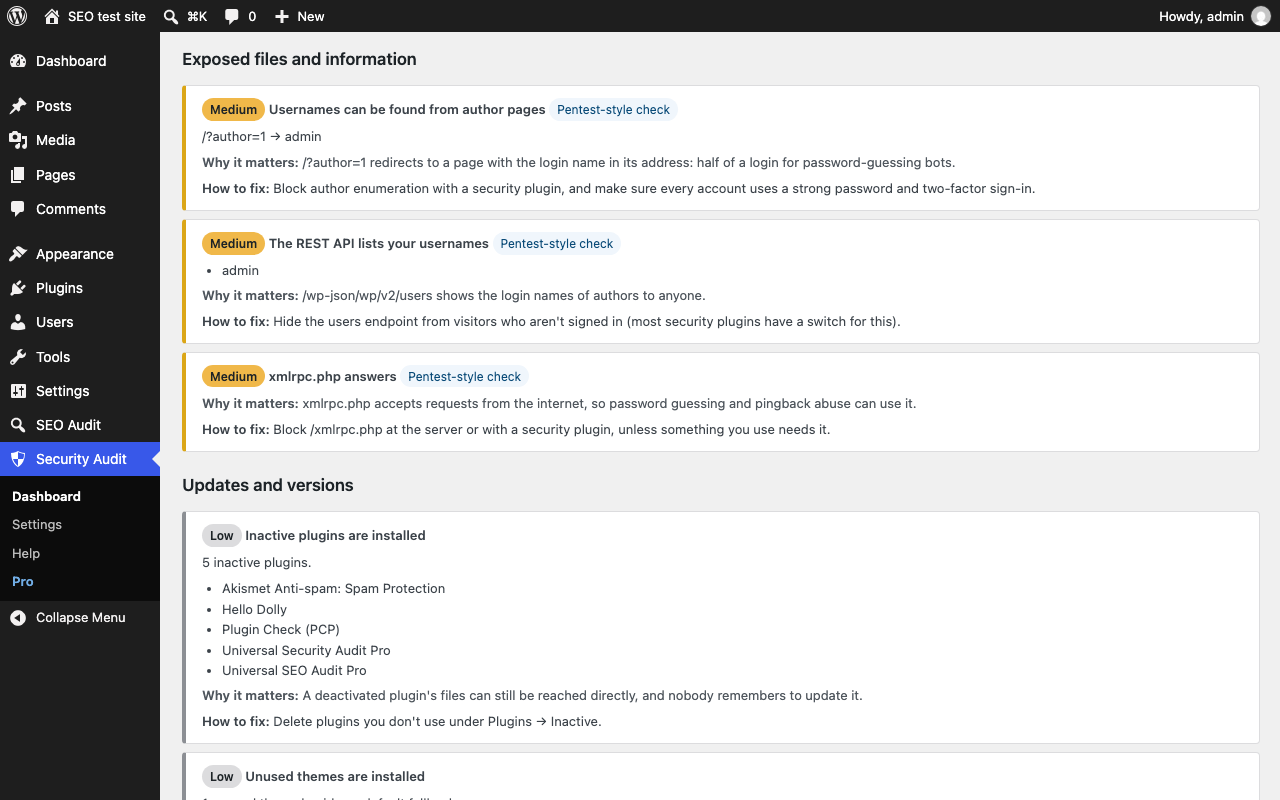
Pentest-style findings, marked as such, each with the fix. 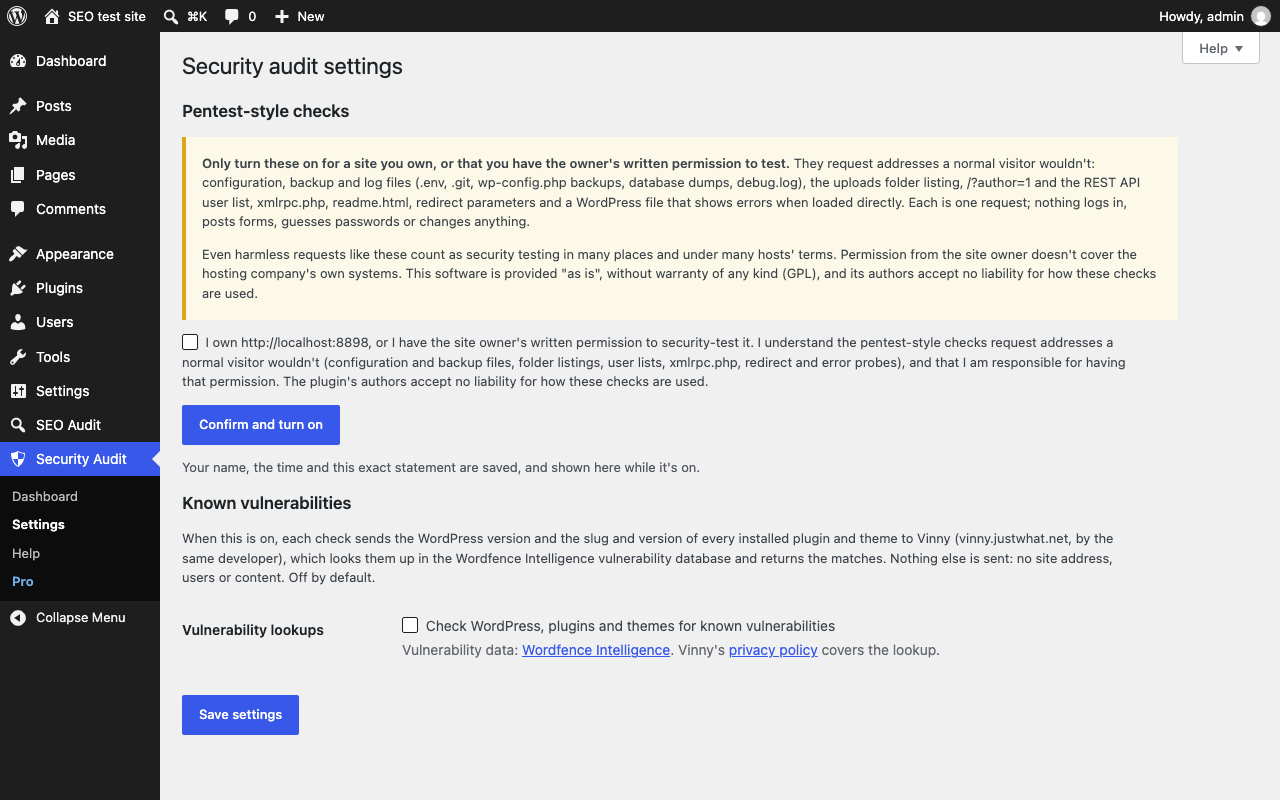
Settings: the written-permission statement and the vulnerability lookup switch.
Three kinds of checks, two of them off until you say so
Always on
Passive checks
What WordPress knows about itself (updates, PHP, settings, users, file permissions) and your home page and security.txt as any visitor gets them.
Off until you confirm permission
Pentest-style checks
Requests to your own site that a normal visitor wouldn't make: exposed files, folder listings, user lists, xmlrpc.php, redirect and error probes. One request each; nothing logs in, guesses passwords or changes anything.
Off until you turn it on
Known vulnerabilities
Every installed plugin, theme and WordPress itself, checked against the Wordfence Intelligence database through Vinny. Only slugs and versions are sent.
Free plugin
What it checks
Updates and versions
WordPress, plugins and themes with updates waiting, inactive plugins and unused themes, automatic security updates turned off, and a PHP version past its security support.
Risky settings
Open sign-ups that hand out a powerful role, PHP errors shown to visitors, a debug log in a public folder, missing security keys, the file editor, a user called "admin", a world-writable wp-config.php and XML-RPC.
What visitors get
Security headers on your home page (HSTS, frame protection, Content-Security-Policy, nosniff, Referrer-Policy), version numbers shown publicly, and security.txt.
Pentest-style checks, with permission
Exposed .env, .git, wp-config.php backups, database dumps and logs, a listed uploads folder, usernames found through author pages or the REST API, open redirects and error pages. Off until you confirm written permission; your confirmation is recorded.
Known vulnerabilities
Turn it on and every installed plugin, theme and WordPress itself is checked against the Wordfence Intelligence database, with how serious each problem is and the version that fixes it.
A grade and what to fix first
An A+ to F grade on the same scale as Vinny and the command-line scanner, findings sorted by severity, and for each one why it matters and how to fix it.
Pentest-style checks need written permission
Only turn them on for a site you own, or that you have the site owner's written permission to test. In many countries, and under many hosting companies' terms, requests like these count as security testing even when each one is harmless, and testing without permission can be illegal. Permission from a site's owner doesn't cover the hosting company's own systems.
They stay off until an administrator ticks the written-permission statement in the plugin's Settings. The plugin saves who agreed, when and the exact statement, and asks again if the site moves to a new address. Withdrawing permission is saved too.
The plugin is free software provided "as is", without warranty of any kind (GPL). Its authors accept no liability for any damage or claim arising from its use; you are responsible for having permission for the checks you run. No automated check finds every problem, and a clean result doesn't mean a site is secure.
Pro add-on
Checked from outside too, on a schedule
WordPress can only see itself from inside the server. Pro adds Vinny's view from the internet's side, through your CDN or firewall, runs both on a schedule, and tells you when something new and serious appears.
Checked from outside, the way visitors reach you
Vinny looks at your site through your CDN or firewall: the security headers and cookies visitors actually get, which replace what WordPress can see from inside the server.
HTTPS, TLS and email records
The certificate (untrusted, expiring, expired), old TLS versions still accepted, and the SPF and DMARC records that stop others sending email as your domain.
What your pages load
JavaScript libraries with known vulnerabilities, scripts from other sites without integrity checks, keys left in JavaScript, published source maps and open admin tools.
Known vulnerabilities for everything installed
With lookups on, WordPress and every installed plugin and theme are checked against the Wordfence Intelligence database with each full check, even ones no page loads.
On a schedule, with alerts
Daily, weekly or every 30 days. An email right after a check finds a new critical or high problem, and a weekly summary.
History and client report
What was new or fixed in each check, a grade trend, and a printable report with your name and logo.
Pricing
One yearly price per plan. Every Pro plan has every Pro feature; plans differ only in how many sites. Licensed separately from the other Pro plugins and from the Vinny web app.
Free
For checking any site, as often as you like.
$0
- Updates, PHP and risky settings
- Security headers and security.txt
- Pentest-style checks, with your permission
- Known vulnerabilities (Wordfence data)
- A grade and how to fix each finding
Pro Personal
One website you run yourself.
$79 / year
1 site
- Everything in Free, plus:
- Scheduled full checks, inside and outside
- Headers and cookies as visitors get them
- HTTPS certificate, TLS and email records
- Vulnerable scripts on your pages
- History, alerts and weekly summary
- Client report
- A year of updates and priority support
Pro Business
Most popularA business with a few sites, or a freelancer.
$199 / year
5 sites
- Everything in Free, plus:
- Scheduled full checks, inside and outside
- Headers and cookies as visitors get them
- HTTPS certificate, TLS and email records
- Vulnerable scripts on your pages
- History, alerts and weekly summary
- Client report
- A year of updates and priority support
Pro Agency
Agencies and teams managing client sites.
$399 / year
Unlimited sites
- Everything in Free, plus:
- Scheduled full checks, inside and outside
- Headers and cookies as visitors get them
- HTTPS certificate, TLS and email records
- Vulnerable scripts on your pages
- History, alerts and weekly summary
- Client report
- A year of updates and priority support
Prices in US dollars, billed yearly; sales tax added where it applies. Cancel any time. 14-day money-back guarantee.
Questions
Is it a firewall or malware scanner?
No. It finds weaknesses before someone uses them: out-of-date code, risky settings, exposed files. Keep your security plugin or your host's firewall for blocking attacks and scanning files.
What are the pentest-style checks, and why are they off?
They make requests to your own site that a normal visitor wouldn't (configuration and backup files, folder listings, user lists, redirect and error probes): the first step of a penetration test. Even harmless requests like these count as security testing in many places, so they stay off until an administrator confirms they own the site or have the owner's written permission. The plugin keeps who confirmed, when and the exact statement.
Can I use it on a client's site?
The always-on checks, yes. For the pentest-style checks, get the owner's written permission first, and remember it doesn't cover the hosting company's own systems. You're responsible for having permission; the plugin is provided as is, without warranty, and its authors accept no liability for how it's used.
Is anything sent outside my site?
Only if you turn on known-vulnerability lookups: the WordPress version and each plugin's and theme's slug and version go to Vinny, which matches them against the Wordfence Intelligence database. No site address, users or content.
My CDN adds security headers, but the plugin says they're missing.
The plugin requests your home page from the server, which can go around a CDN or firewall in front of the site. Visitors still get the CDN's headers.
Is the free plugin really free?
Yes. Nothing in it is locked, time-limited or nagging. Pro is a separate add-on for sites that need security checked continuously, from outside as well as inside.
Where do Pro's outside checks run?
On Vinny, our servers: the plugin sends your license key, the public address and, when you turn them on, your recorded permission and the list of installed plugins and themes. Vinny checks the site from the internet's side and the results come back into WordPress. Vinny deletes its copy after 30 days.
Is a license shared with the other Pro plugins?
No. Each Pro plugin has its own license, bought separately, at the same prices.
What if I'm not happy?
Ask for a refund within 14 days of purchase and you'll get it, no questions asked.
The free command-line scanner runs the same kind of checks on any site, in CI too, with the same permission rule for its active checks (--authorized).
Find out where your site stands in five minutes
Install the free plugin, pick a few pages and run your first scan. No account, no setup.